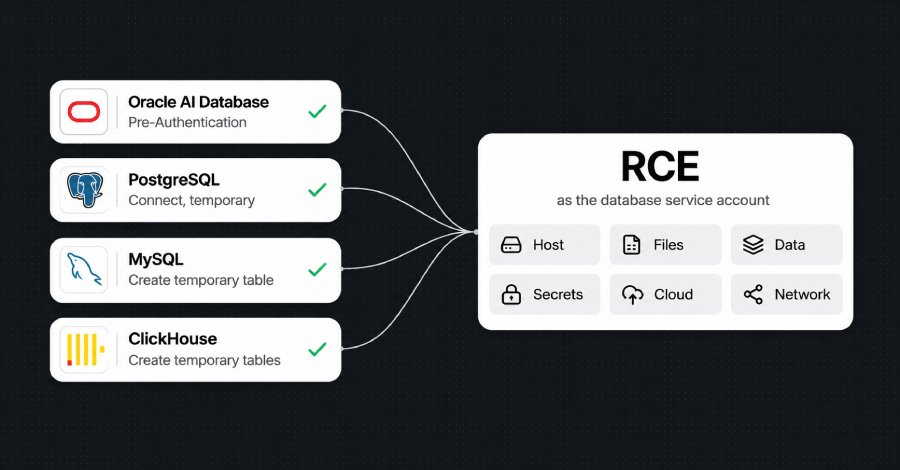
Low-privilege database accounts that cannot read a single application table can still be used to run code on the database server itself, a researcher has shown, by reaching memory-corruption bugs in the engine code behind ordinary SQL.
The exploits, published yesterday, are the researcher’s proofs of concept against PostgreSQL, MySQL and ClickHouse, plus a separate Oracle chain that needs no Low-privilege database accounts that cannot read a single application table can still be used to run code on the database server itself, a researcher has shown, by reaching memory-corruption bugs in the engine code behind ordinary SQL.
The exploits, published yesterday, are the researcher’s proofs of concept against PostgreSQL, MySQL and ClickHouse, plus a separate Oracle chain that needs no The Hacker News