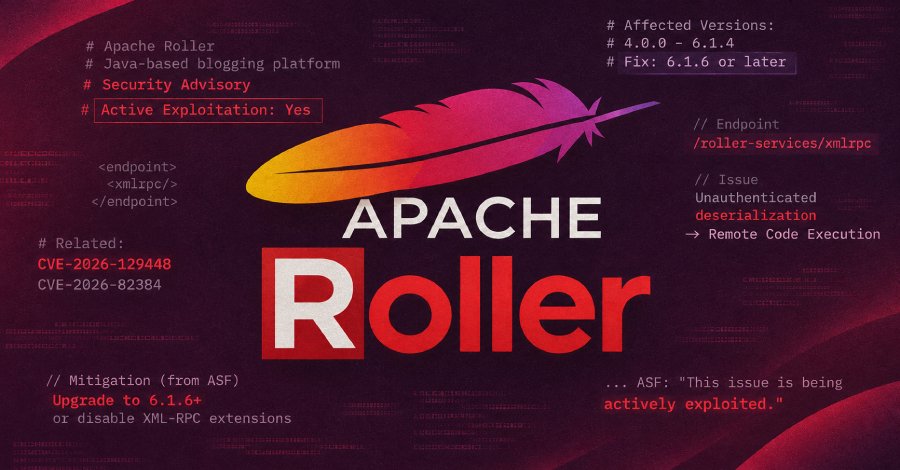
Critical Apache Roller RCE Flaw Under Active Exploitation, No Authentication Required
A critical security flaw in Apache Roller, an open-source, Java-based blogging platform, has come under active exploitation in the wild, according to the Apache Software Foundation (ASF) The vulnerability, tracked… Read More »Critical Apache Roller RCE Flaw Under Active Exploitation, No Authentication Required